Cyber Risk, Operational Resilience, Third Party Risk The Exposure You Do Not Own: What the European Refrigeration Attacks and PHP2Shell Teach Boards About Resilience
Board Governance, Cyber Risk The Board’s Cyber Mandate: Why Director-Level Cyber-Risk Oversight Is Now a Fiduciary Imperative
AI Governance, Risk Management The Trust Architecture Deficit: Why AI Governance Is Redefining Enterprise Risk Oversight and Assurance in 2026
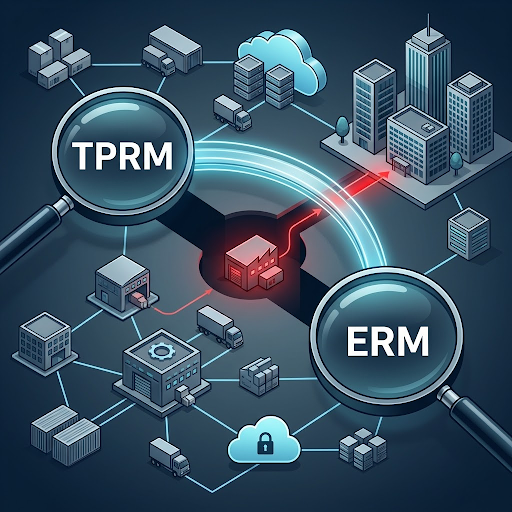
Cybersecurity, Risk Management The Third-Party Blind Spot: Why TPRM and ERM Must Speak the Same Language Before the Next Supply Chain Breach
Governance, Risk Management Governing the Autonomous Enterprise: Why Trust Architecture Is Now the Cornerstone of ERM, Cybersecurity, and Assurance
Risk Management Governing What You Cannot See: Agentic AI, Non-Human Identities, and the New Frontier of Enterprise Assurance
Operational Resilience One Flaw, a Hundred Victims: What the Oracle PeopleSoft Zero-Day Reveals About Enterprise Platform Risk
Risk Management When AI Becomes a Liability: What Florida’s OpenAI Lawsuit Means for Enterprise Leaders